Legal
DPDP Act for PG Owners: How to Store Tenant Aadhaar and KYC Legally
Written by
Ishika Pannu
Read Time
13 min read
Posted on
October 25, 2026
Overview
Overview
DPDP Act for PG Owners: How to Store Tenant Aadhaar and KYC Legally
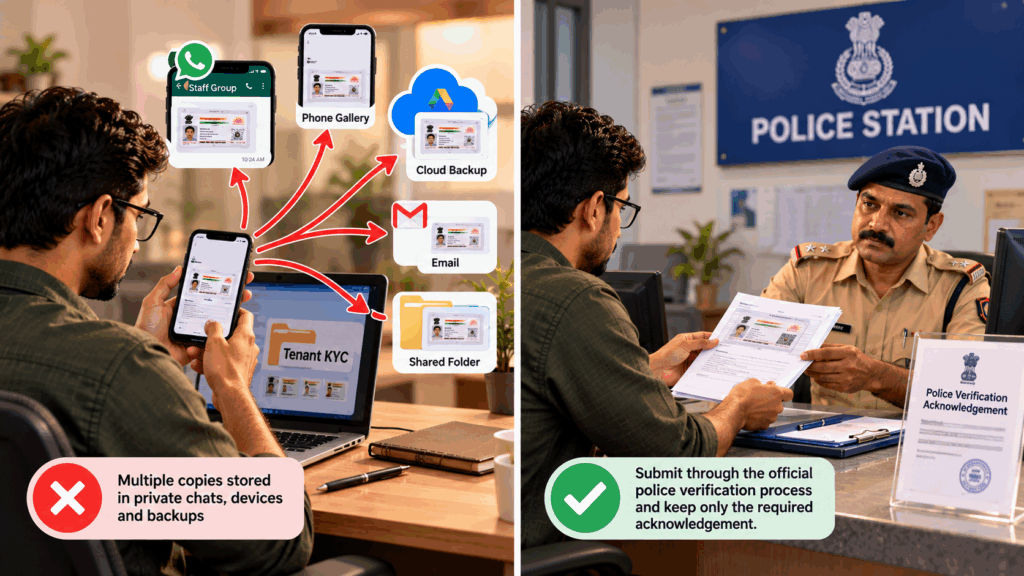
A tenant sends an Aadhaar image to the manager. The manager forwards it to the owner, downloads it for police verification and leaves another copy in a cloud backup. Months after the tenant moves out, the business may still hold several copies without knowing who can access them or why they remain.
Understanding the DPDP Act for landlords starts with those everyday decisions. You need a clear reason to collect information, a controlled place to keep it and a process for reviewing retention. You also need to distinguish Aadhaar rules that already apply from DPDP obligations that start in phases. This guide explains that difference and turns it into a practical tenant KYC workflow for PG owners.
Why your PG counts as a data fiduciary
The Digital Personal Data Protection Act, 2023 calls the person deciding why and how to process personal data a Data Fiduciary. A PG operator who chooses the information collected during onboarding and how the business uses it will generally fit that role. The tenant is the Data Principal.
The Act’s scope covers digital personal data, including paper information that you later digitise. A photographed ID, onboarding form, tenant spreadsheet or scanned register can therefore fall within the framework when its substantive provisions commence. A purely paper record that never enters digital form falls outside that scope, although other legal and confidentiality duties may still apply.
For practical purposes, treat digital KYC as a structured onboarding process rather than a collection of ID pictures. Record what you need, who may use it and when to review it. A cloud platform or verification vendor can support the work, but outsourcing storage does not automatically transfer the owner’s responsibility.
Key dates every owner should know
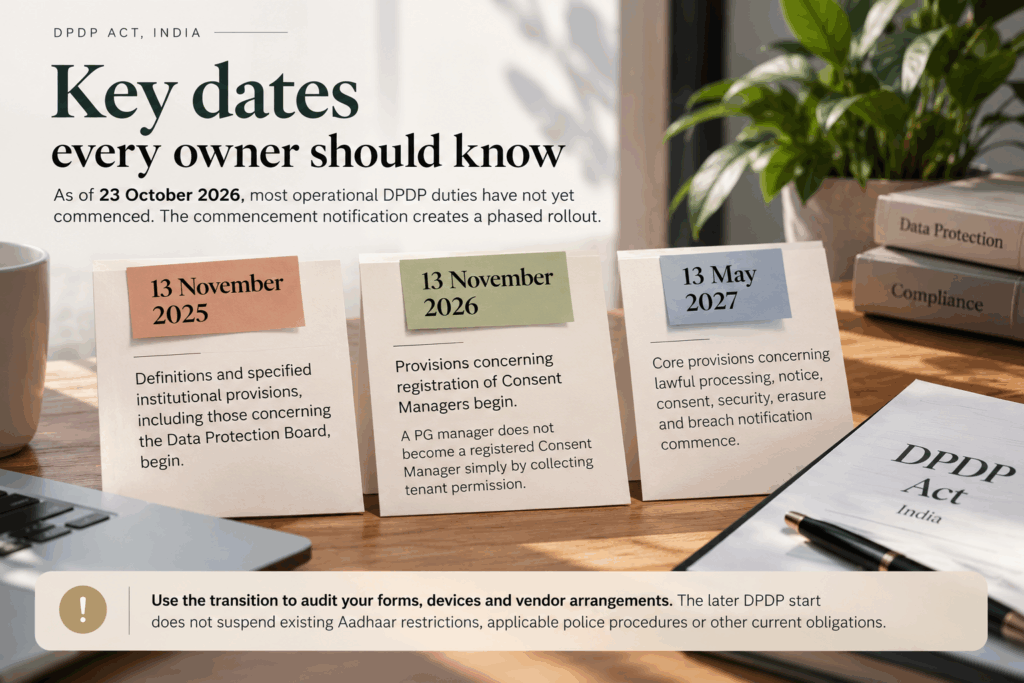
As of 23 October 2026, most operational DPDP duties have not yet commenced. The commencement notification creates a phased rollout; the table follows the commencement dates recorded in India Code.
| Date | What it means for PG owners |
|---|---|
| 13 November 2025 | Definitions and specified institutional provisions, including those concerning the Data Protection Board, begin. |
| 13 November 2026 | Provisions concerning registration of Consent Managers begin. A PG manager does not become a registered Consent Manager simply by collecting tenant permission. |
| 13 May 2027 | Core provisions concerning lawful processing, notice, consent, security, erasure and breach notification commence. |
Use the transition to audit your forms, devices and vendor arrangements. The later DPDP start does not suspend existing Aadhaar restrictions, applicable police procedures or other current obligations. In the sections below, references to the new DPDP operational duties describe what owners should prepare to meet when those provisions commence.
What tenant data you can and cannot collect
Build a purpose-based KYC form
Start with the purpose of each field, not every document a previous manager happened to request. For an ordinary onboarding workflow, consider the tenant’s name, contact details, address, room allocation and occupancy dates. Collect a photograph, age information or emergency contact only where you can explain the need or an applicable requirement calls for it.
| Information | Practical collection decision |
|---|---|
| Identity and address | Verify through an accepted document; record necessary details and the verification outcome. |
| ID-document copy | Retain only where justified and lawful; do not assume every identity check needs a permanent scan. |
| Emergency contact | Explain its emergency purpose and limit access. Ask tenants to inform the person whose details they provide. |
| Payment records | Keep relevant transaction and settlement evidence without treating an Aadhaar scan as an accounting requirement. |
| Unrelated personal information | Remove fields such as social-media passwords or a phone contact list from routine housing onboarding. |
Offer viable identity alternatives, such as a passport, voter ID or another document accepted for the relevant process. PAN does not establish an address, so do not assume every government ID supplies the same information.
Follow the Aadhaar-specific restrictions
For ordinary private PG verification, do not make Aadhaar authentication or offline verification the only route when the resident can identify themselves through a viable alternative. Under UIDAI’s authentication and offline-verification regulations, offline verification requires consent and verification of UIDAI’s digital signature; receiving a photo does not complete that check.
An Offline Verification Seeking Entity, or OVSE, cannot freely collect or store full Aadhaar numbers or biometrics. The regulations permit secure storage of permitted offline Aadhaar data with consent, subject to UIDAI requirements. That is different from maintaining an unrestricted folder of unmasked cards.
Where appropriate, prefer a verification record and necessary demographic details over an unnecessary full-card image. Masked Aadhaar hides the first eight digits, but masking alone does not establish a purpose, consent or authority to retain a copy. Never ask a resident to share an Aadhaar OTP with staff as an informal verification shortcut.
Make tenant KYC consent specific
Under the forthcoming framework, consent is one lawful ground, not the only ground. The Act also permits specified legitimate uses, including certain voluntarily supplied information and legally required disclosures to the State. Identify the applicable ground for each activity rather than using one blanket checkbox for everything.
Where you rely on tenant KYC consent, explain the data, purpose and relevant sharing in plain language. The government’s DPDP overview emphasises clear notices and purpose limitation. Keep optional marketing separate from housing administration, and provide a contact for questions, correction requests and withdrawal where applicable.
An illustrative starting point for a notice is:
We collect your name, contact details, address and necessary identity-verification information to administer your stay. We submit required information to the relevant police authority where applicable. Contact [name/contact] about your information or consent choices. Our retention schedule explains what we keep and why.
Adapt this wording to your actual workflow; it is not a complete legal notice. For residents under 18, plan for the Act’s child-data provisions and verifiable parental consent when applicable. Do not treat a student’s college admission as proof of adulthood.
The Aadhaar-on-WhatsApp problem
Control copies, not just the original message
The issue is not a blanket rule that WhatsApp is illegal for tenant communication. The practical problem is the spread of identity files through downloads, forwarded messages, linked devices and backups. Message encryption does not control every copy that staff create after receiving a document.
Replace informal forwarding with a defined workflow:
- Explain the purpose before collection. Tell the tenant which details you need and offer the appropriate submission route.
- Verify, then minimise. Keep the necessary verification result or lawfully required record instead of making convenience copies.
- Restrict access by task. A staff member arranging meals or cleaning does not ordinarily need to download identity documents.
- Review every copy location. Check phone galleries, email attachments, shared folders, old devices and backups before declaring a record removed.
If you are moving tenant operations beyond spreadsheets, include this copy audit in the migration. Uploading files to a new platform while leaving old versions everywhere does not create a controlled records system.
Keep police verification separate from private storage
Identity verification and police verification serve different purposes. A valid ID does not prove that staff completed the local submission procedure, and a police acknowledgement does not authorise unlimited private retention.
Check the current procedure for the property’s jurisdiction. Delhi Police’s Citizen Charter describes the owner’s obligation to inform local police when keeping a tenant; Haryana Police lists a Tenant/PG Verification service. Bengaluru, Pune, Hyderabad and Gurugram owners should check their respective police authority’s current orders, forms and accepted documents rather than assume one national mandate or deadline.
Use the official route, record the submission reference and retain the evidence actually required. A legal obligation to disclose particular information does not automatically justify extra unencrypted copies in a staff group. Check the scope of any police request or retention instruction before deciding what to preserve.
How long can you keep data after move-out?
Avoid both indefinite storage and automatic deletion
There is no universal DPDP rule to delete every tenant record on the move-out date. Purpose-based erasure must work alongside legal retention duties. The final DPDP Rules, 2025 add an important qualification: Rule 8(3) requires retention of personal data, associated traffic data and processing logs for at least one year from the processing, for the Seventh Schedule purposes, once that rule commences.
That is not a universal “one year after move-out” period, nor permission to collect prohibited Aadhaar information. The Rules also contain security-related retention requirements. Have your retention schedule reconcile those provisions with UIDAI restrictions, police requirements and other applicable law.
| Record category | What your schedule should establish |
|---|---|
| Verification details and permitted KYC records | Purpose, applicable minimum retention, access restrictions and review date. |
| Agreement, payments and settlement records | Relevant accounting, contractual and legal requirements; retain the necessary evidence. |
| Police submissions and acknowledgements | Applicable procedure, retention instruction and any active investigation requirement. |
| Records subject to a dispute or preservation requirement | Defined legal hold, restricted access and a date to review whether the hold continues. |
| Unnecessary duplicate files | Remove where lawful after checking evidence and retention needs across devices and backups. |
Make retention review part of the exit process
Add a data review to your move-in and move-out workflow. Record the exit date, complete settlement, identify any continuing legal purpose and schedule the next review. “We might need it someday” should not become an indefinite retention policy.
Keep handover and settlement documentation distinct from unnecessary identity scans. A rent receipt or damage record may support a dispute without requiring every ID image collected at joining. Apply appropriate controls to retained paper files too, and shred them when their lawful retention ends.
Ask your platform provider how deletion requests, legal holds and backups interact. Deleting a visible profile may not remove exports or every backup immediately; document the actual process rather than promising instant, complete erasure.
What to do if tenant data leaks
Contain the incident and preserve evidence
A lost staff phone, public folder link or wrongly forwarded KYC attachment needs prompt attention. Stop further exposure, revoke affected access, secure accounts and ask the platform provider to preserve relevant logs. Record what happened, when staff discovered it, which records may be involved and who received them.
Do not mass-delete evidence to make the problem disappear. Assign one incident lead, investigate the scope and give affected tenants accurate practical information. Avoid promises such as “nothing can happen” before you know the facts.
Check each reporting duty separately
When the DPDP breach provisions commence, Rule 7 requires notification to affected individuals and the Board without delay, followed by detailed information to the Board within 72 hours, unless it permits a longer period. The 72-hour period is not permission to postpone the first notification.
Existing regimes may act sooner. CERT-In’s directions require covered entities to report specified cyber incidents, including data breaches or leaks, within six hours of noticing them or receiving notice. Check whether your entity and incident fall within those directions.
For an OVSE, UIDAI’s breach rules separately require reporting Aadhaar-related compromise without undue delay and no later than 72 hours after knowledge, with relevant affected-holder notification duties. Keep these obligations distinct: reporting to one authority does not automatically satisfy another. Establish the applicable notifications with your incident adviser immediately.
A simple compliance checklist for PG owners
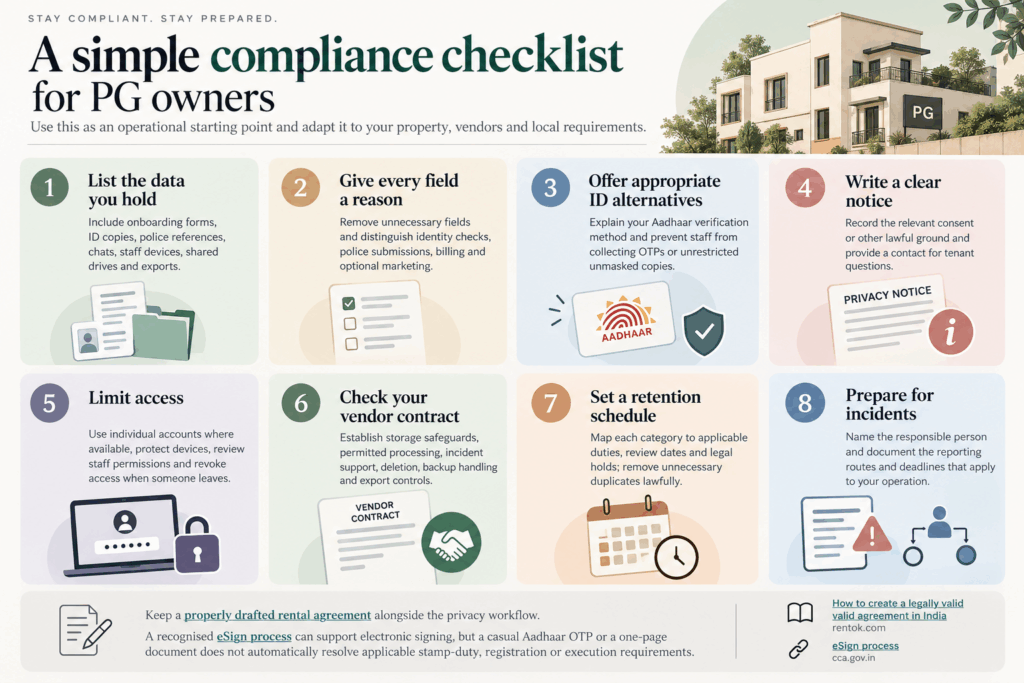
Use this as an operational starting point and adapt it to your property, vendors and local requirements:
- List the data you hold: Include onboarding forms, ID copies, police references, chats, staff devices, shared drives and exports.
- Give every field a reason: Remove unnecessary fields and distinguish identity checks, police submissions, billing and optional marketing.
- Offer appropriate ID alternatives: Explain your Aadhaar verification method and prevent staff from collecting OTPs or unrestricted unmasked copies.
- Write a clear notice: Record the relevant consent or other lawful ground and provide a contact for tenant questions.
- Limit access: Use individual accounts where available, protect devices, review staff permissions and revoke access when someone leaves.
- Check your vendor contract: Establish storage safeguards, permitted processing, incident support, deletion, backup handling and export controls.
- Set a retention schedule: Map each category to applicable duties, review dates and legal holds; remove unnecessary duplicates lawfully.
- Prepare for incidents: Name the responsible person and document the reporting routes and deadlines that apply to your operation.
Keep a properly drafted rental agreement alongside the privacy workflow. A recognised eSign process can support electronic signing, but a casual Aadhaar OTP or a one-page document does not automatically resolve applicable stamp-duty, registration or execution requirements.
How RentOK helps owners organise tenant KYC
For a PG owner, the practical problem is keeping tenant information connected to the correct resident without relying on scattered staff chats. RentOK offers digital check-in, tenant profiles and document review to support that workflow:
- Structured onboarding: Bring resident and rental details into a defined record so staff can review the information collected for that stay.
- Document review: Use the ability to verify or reject submitted government IDs and documents as part of your chosen process. Confirm the underlying verification method before describing it as UIDAI authentication.
- Connected rental records: Keep occupancy and payment information linked to the resident, reducing the need to circulate ID images for routine billing questions.
- A published privacy and deletion route: RentOK’s privacy policy describes security measures and allows personal-data deletion requests through the app or support. Check how those requests interact with required retention and backups.
Before uploading KYC records, confirm the access settings, contractual safeguards and incident-support process for your account. The platform supports record management; your collection choices, staff practices and retention decisions still determine how you handle tenant information.
Conclusion
Good tenant data protection in India begins with a smaller, better-controlled record: collect for a defined purpose, follow the applicable Aadhaar process, complete local police submissions separately and know who can access each file. Plan retention by record category rather than keeping everything forever or deleting everything at move-out.
Use the DPDP transition to put those decisions into everyday practice. If you want to store tenant KYC securely on RentOK, review its privacy terms and confirm the controls your PG needs before migrating records. Explore RentOK’s tenant KYC workflow and build it around your notice, access and retention policy.
Frequently Asked Questions
Find answers to common questions about this topic
About the Author
Ishika Pannu
Ishika Pannu brings you the latest insights and easy-to-apply strategies in property management—helping you simplify renting and grow with RentOk.